AI Agent Development
Custom enterprise AI agents built with security-first architecture. From MCP integrations to autonomous workflows.
Learn MoreArgent Strategic Intelligence, from Nyedis, is one checkpoint between your AI agents and everything they touch. It shows you every agent by name, signs a record of every decision, and stops anything you did not approve before customer data or money leaves.
20+ Years Enterprise Security Experience
From IAM architects to AI pioneers. We bring two decades of enterprise security expertise to agent development, governance, and integration.
What We Do
Custom enterprise AI agents built with security-first architecture. From MCP integrations to autonomous workflows.
Learn MoreIAM-grade security for AI systems. Access controls, audit logging, and compliance frameworks for agent deployments.
Learn MoreConnect AI to your existing stack. BigQuery, Kubernetes, cloud platforms—unified through secure, standardized protocols.
Learn MoreRoadmaps that deliver ROI. We help enterprises navigate the AI landscape with proven frameworks and hands-on expertise.
Learn MoreOur Foundation
Nyedis started as pioneers in Identity & Access Management, protecting enterprises from the inside out. When AI emerged as the next frontier, we brought that same security-first mindset to agent development.
We don't just build AI—we build AI that enterprises can trust. Every agent we deploy carries 20 years of lessons learned from securing the world's most demanding organizations.
Latest Insights
Ready to Transform
Whether you're starting your AI journey or scaling existing deployments, we bring the expertise to make it work—securely.
Argent Strategic Intelligence: Master Control System, by Nyedis
It is the control point that sits between every AI agent and the AI it talks to, so a company can see every agent, prove every decision with signed evidence, and stop anything it did not approve.
Four things go wrong when AI agents run loose. Customer data leaves through an agent. A regulator asks which agent did what, and nobody can say. An agent keeps running after its owner has left. A bill climbs every hour, and nobody owns it. Argent closes all four.
In plain words
Six areas of control
Mark the areas your company already handles today. Whatever is left becomes your shortlist for the demo.
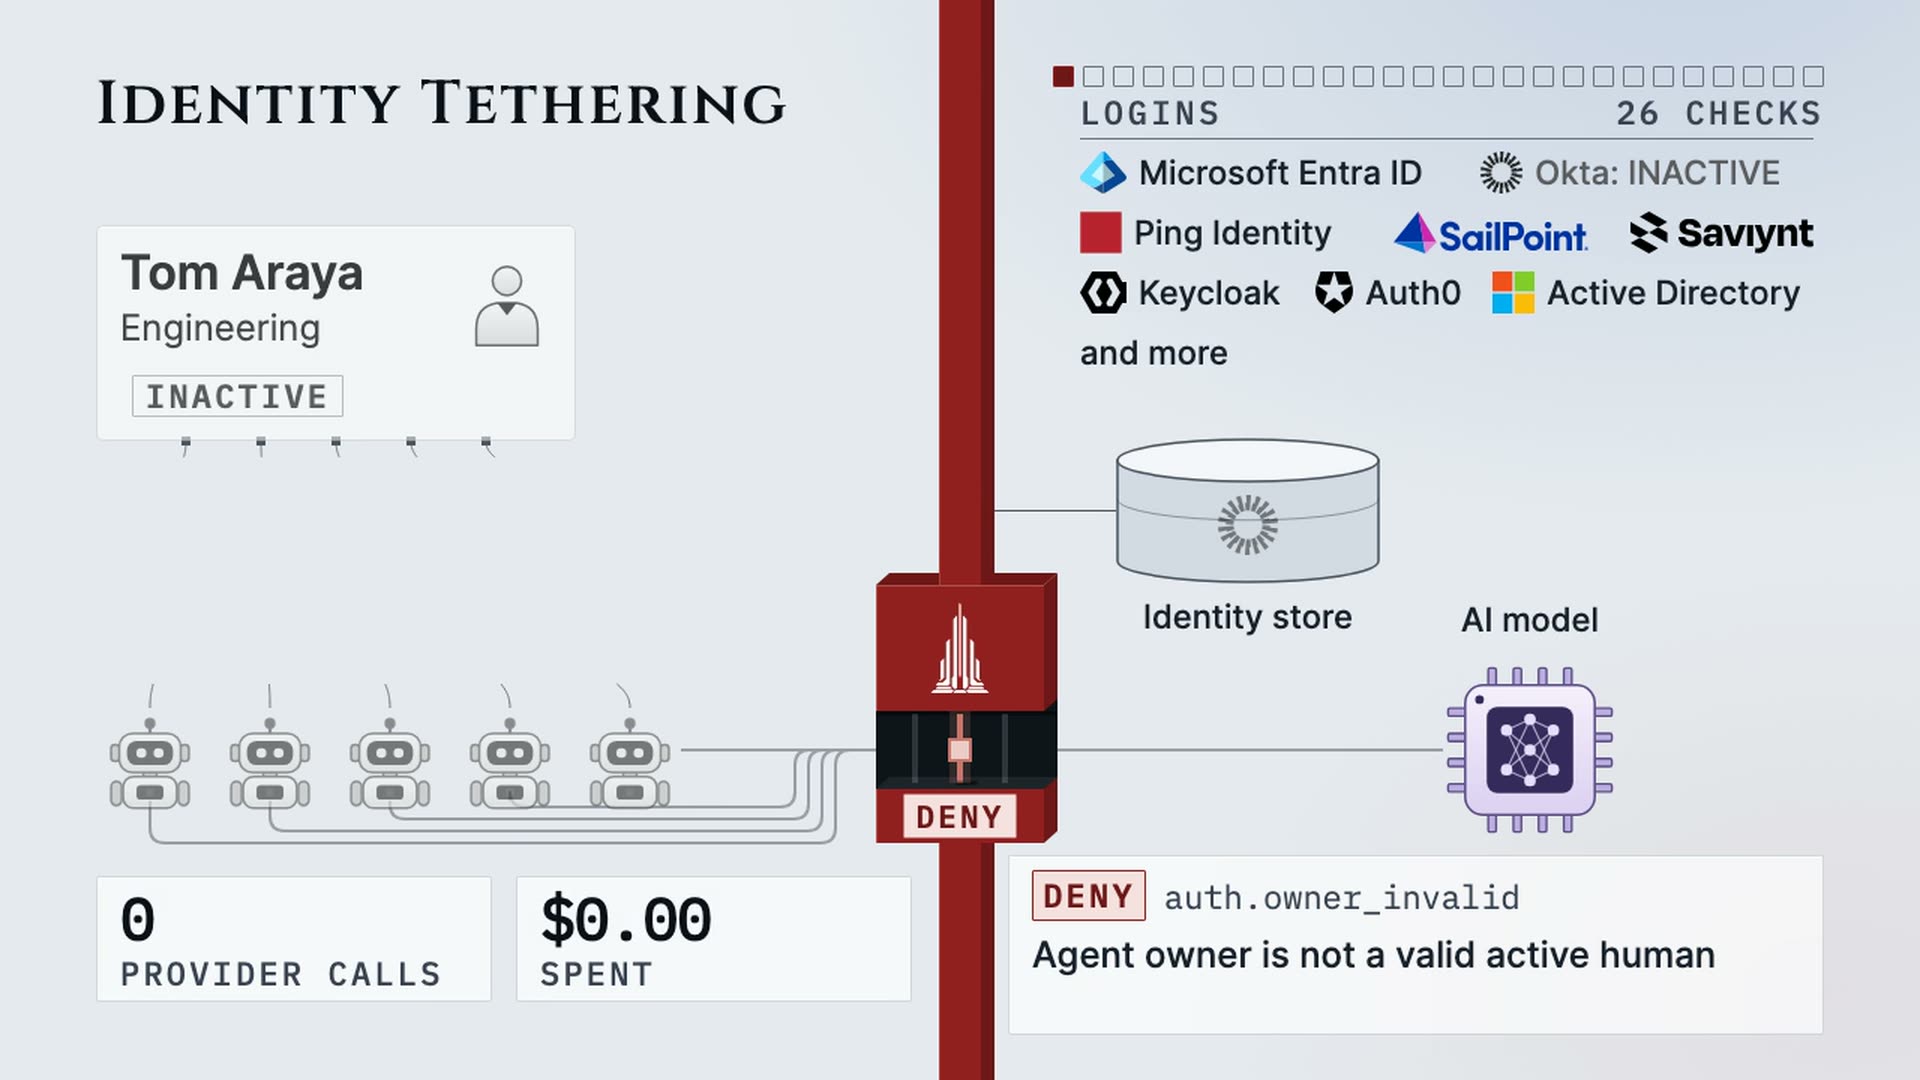
What goes wrongA contractor quits, his agents keep running, and nobody can say which agent did what.
What Argent doesEvery agent has a named human owner pulled from your login system. When that person leaves or is switched off, the agent’s very next request is blocked. All your agents show on one screen, by name, with a dollar tag.
invoice-botowner switched offDENYauth.owner_invalid$0.00
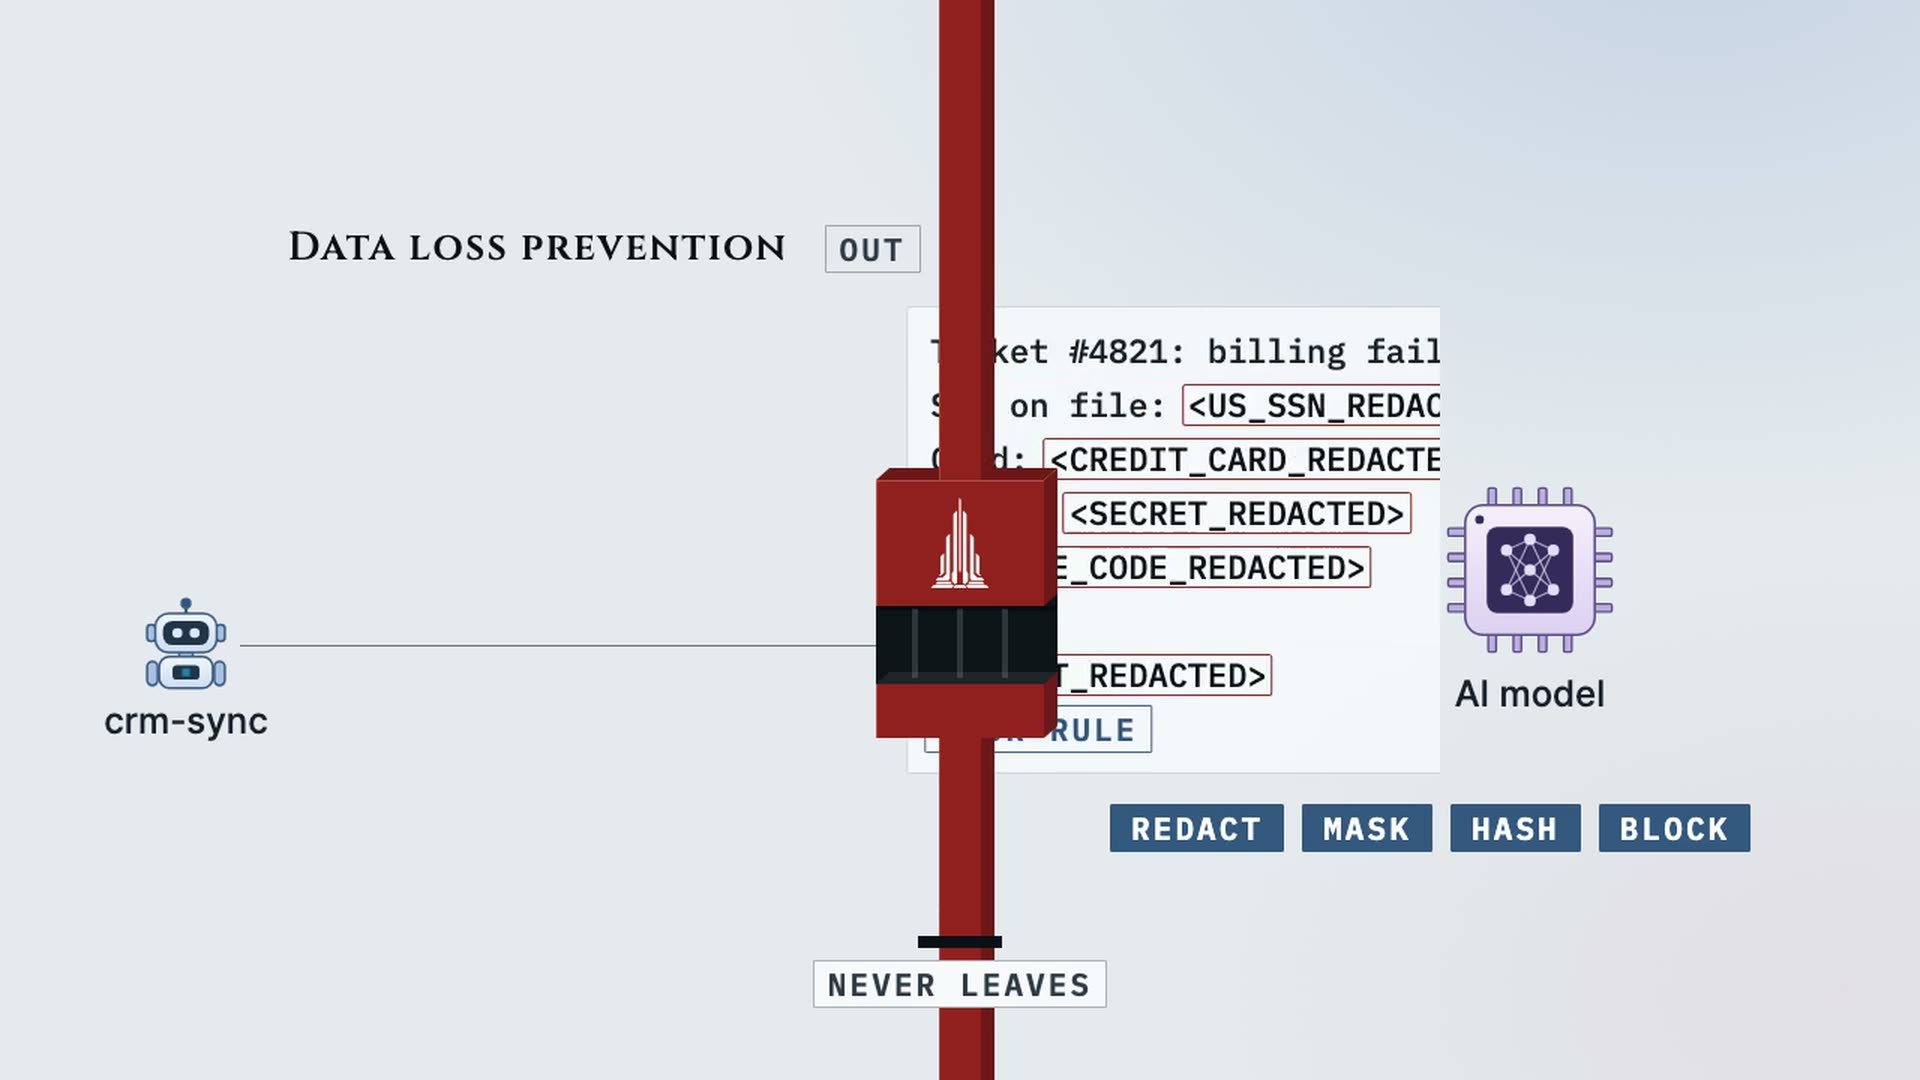
Watch this part of the film (01:20)What goes wrongCustomer files, secrets and source code get sent to an AI nobody approved.
What Argent doesArgent reads every outgoing message and replaces Social Security numbers, card numbers, API keys, source code and your own secret formulas with placeholders before the AI sees them. The answer coming back is scanned too.
report-genSSN replaced by a placeholderMASKEDdlp.piisigned
Watch this part of the film (01:49)What goes wrongAn agent reaches a tool, a document or another agent it was never meant to touch.
What Argent doesAgents call only the tools you approved: reading a file yes, deleting your code never. Document search returns only what the person behind the agent may read. Messages between agents follow the same rules, and the default answer is no.
code-helperdelete repositoryDENYmcp.tool_not_approved$0.00
Watch this part of the film (03:14)What goes wrongA real provider key sits in an agent’s settings, leaks, and runs up charges nobody can trace.
What Argent doesPeople and agents never hold real provider keys. They sign in to Argent, which adds the real key from your own vault. Argent holds a path to the secret, never the secret itself.
crm-syncreal key added from your vaultALLOWcred.injectedkey not exposed
Watch this part of the film (03:23)What goes wrongAgents nobody owns spend a little more every hour.
What Argent doesEvery company, department, person and agent gets a dollar limit. Argent holds the money up front, settles the real cost after, forecasts when a team will run out, and stops a runaway loop at the cap: $25, not $25,000.
ticket-triagedaily cap reachedCAPbudget.cap_reachedstopped
Watch this part of the film (02:13)What goes wrongA regulator, board or court asks which agent did what, on whose authority, and when.
What Argent doesEvery allow, deny, redact and quarantine is a signed, chained record in a write-once archive. A separate program verifies the whole chain offline, and builds an evidence bundle for your SOC 2 auditor in under 30 seconds.
ledgerevery decision recordedSIGNEDchain verifiedoffline
Watch this part of the film (03:49)Argent covers all six, and signs every decision.
Book a DemoHow one request flows
Interactive walkthrough
A narrated walkthrough of Argent in three parts: the product, one request through all 51 checks, and where it runs on Kubernetes or Docker Compose. About 13 minutes, and it plays right in your browser on desktop or phone.
Every control, explained
Works with your stack
Twenty-three AI tools proven live, dozens more supported.
Plus any tool that speaks the OpenAI, Anthropic, Gemini or Bedrock wire format or honors a proxy setting, and any MCP server or A2A agent. Native SDKs for Python, Node and Go.
Plus any OpenAI-compatible endpoint, with thousands of priced models.
Plus any identity system that speaks SCIM or LDAP. Operators sign in with passkeys.
Bring your own vault. Argent holds a path to the secret, never the secret itself. 23 vault connector types in all.
Or bring your own Open Policy Agent bundles.
Plus a bridge for your own guardrail.
Audit events leave as signed webhooks to any HTTPS endpoint (Slack included).
Four sizing tiers, small to extra large.
Deploy
Run the full stack on a local machine in 2 minutes, with one command.
Deploy to your own cloud in about 20 minutes: Docker Compose, one Helm chart for Kubernetes, AWS, Azure and Google Cloud profiles, or your own data center.
No internet and no API keys are needed at runtime, and nothing phones home. Run fully air-gapped, even on your own models.
Open source core under Apache-2.0: the gateway, filter chain, MCP proxy, agent-to-agent governance, offline verifier and signed audit chain.
Who built it
Built by a team of enterprise identity and access security experts. Over twenty years inside major financial institutions. Government agencies. Healthcare and higher education.
See every agent. Prove every decision. Stop anything you didn't approve.
Argent Strategic Intelligence
Our Services
From strategy to deployment, we bring 20 years of enterprise security expertise to every AI engagement. Security isn't an afterthought—it's our foundation.
Custom Enterprise Agents Built for Scale
We design and build AI agents that integrate seamlessly with your enterprise stack. From MCP-compliant tool integrations to autonomous workflow orchestration—built with security-first architecture.
Discuss Your ProjectIAM-Grade Security for AI Systems
Two decades of identity management expertise applied to AI. We implement access controls, audit logging, and compliance frameworks that bring enterprise-grade security to your agent deployments.
Discuss Your ProjectConnect AI to Your Existing Stack
Unify AI agents with your enterprise infrastructure. We handle BigQuery, Kubernetes, cloud platforms, SaaS tools, and legacy systems—all through secure, standardized protocols.
Discuss Your ProjectRoadmaps That Deliver ROI
Navigate the AI landscape with confidence. We help enterprises define strategy, prioritize use cases, build teams, and establish governance—grounded in hands-on implementation experience.
Discuss Your Project// IDENTITY & CLOUD · 2026
Two decades deep in Identity & Access Management, cloud architecture, and Web3. We don't body-shop and we don't dabble — we master a stack before we adopt the next one. Built for impossible timeframes and budgets.
"Why are you still planning and implementing identity using legacy methods?"
Diagnostic deep-dive on existing identity, access, and cloud security posture. Map controls, gaps, and risk exposure against your operating reality.
Target architecture and roadmap across IAM, IGA, PAM, and cloud security — sequenced for capability uplift, not vendor checklists.
Independent evaluation and selection of identity, PAM, and cloud security platforms — scored against your environment, not analyst quadrants.
Audit of in-flight or live deployments to validate configuration, integration patterns, and operational health before they become incidents.
End-to-end build and integration of IGA, AM, PAM, and orchestration platforms — including connectors, workflows, and policy fabric.
Outsourced and managed operations for identity platforms — day-2 lifecycle, support, tuning, and continuous improvement.
Decentralized identity and blockchain engineering for clients building forward-leaning identity primitives.
// How We Engage
Let's discuss your enterprise AI goals and how we can help you achieve them—securely.
AI Sentinel Protocol
From awareness to autonomy. A progressive security framework that evolves with your AI maturity—protecting agents, data, and decisions at every stage.
The Sentinel Protocol
Progress through each stage as your AI capabilities grow. Start with awareness, evolve to autonomy.
Know What's Coming
Weekly AI threat intelligence and industry briefings. Understand the landscape before it impacts your organization.
Monitor & Detect
Real-time monitoring of your AI deployments. Detect anomalies, policy violations, and security incidents as they happen.
Govern & Control
Full governance framework for AI operations. Ensure every agent action aligns with your security policies and compliance requirements.
Self-Defending AI
AI that protects AI. Autonomous threat response, self-healing systems, and predictive security that evolves with the threat landscape.
Built by security veterans, for the AI era. Protection that understands both threats and technology.
20 years of IAM expertise applied to AI agent governance and protection.
Purpose-built for the unique challenges of AI systems, not retrofitted legacy tools.
From model inputs to agent actions—complete visibility across your AI infrastructure.
Millisecond threat detection and response. Stop attacks before they cause damage.
Our systems learn from global threat patterns. Your security improves automatically.
Built-in frameworks for SOC2, ISO 27001, GDPR, and emerging AI regulations.
Begin with AI Sentinel Aware—weekly intelligence briefings delivered to your inbox. No credit card required.
Get weekly AI security intelligence, threat briefings, and actionable insights delivered to your inbox. Join enterprise leaders staying ahead of AI risks.
Ready for more? Contact us to discuss Active, Aligned, and Autonomous tiers.
// Media · Nyedis Anarchy Series
Unfiltered takes on AI, identity, cloud, and the operators actually shipping the work. No sugarcoating, no vendor talking points — just the signal you don't get from the analyst circuit.
// Episodes
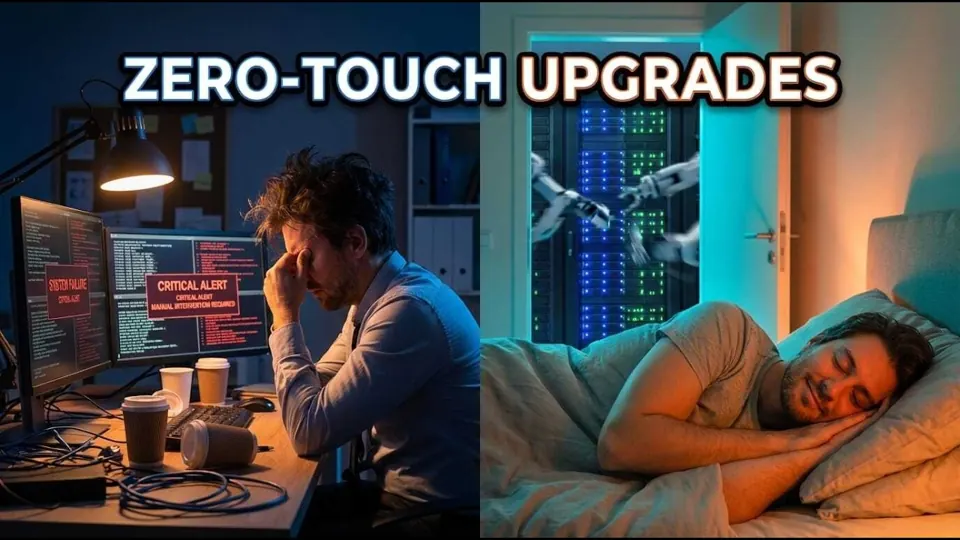
An AI agent that patches servers autonomously with full regression testing and self-healing — detects new Keycloak versions, clones instances, and applies updates.
Watch on YouTube →
Four OpenClaw AI agents connected and self-organized into a coordinated team in real time. Adam unpacks why OpenClaw/Clawdbot is taking off.
Watch on YouTube →
Hands-on with Nvidia's DGX Spark — a compact desktop AI box that lets developers run large memory models, but with real-world speed tradeoffs.
Watch on YouTube →
Nyedis Anarchy Series — a no-sugarcoating take on the accelerating timelines of AI and robotics.
Watch on YouTube →
After an Identiverse epiphany and a year deep in AI, Adam declares the innovation in identity management dead — and shows what's replacing it.
Watch on YouTube →
Brainstorming how AI can be integrated with LDAP to modernize one of identity's oldest workhorses.
Watch on YouTube →
A breakdown of Veza's AIM suite and how it's setting new standards for AI-driven identity management and integrations.
Watch on YouTube →
The destructive grip of screen time on kids — and the transformation boredom can spark when electronics are pulled.
Watch on YouTube →
Why some industries — tattoos, vice, AI — stay recession-proof even when everything else cracks.
Watch on YouTube →
AI's coming impact across the job market — from bartenders to engineers — and why it's not a passing trend.
Watch on YouTube →
Apple's AI news summaries gone off the rails — fake deaths, bizarre headlines, and the dark side of AI-generated news.
Watch on YouTube →
Bypassing Genmoji's content filters on iPhone — a hands-on demo of getting around censored prompts.
Watch on YouTube →Subscribe to the channel for new drops on AI, identity, and the chaos in between.
Insights & Analysis
Deep analysis, actionable frameworks, and security insights for enterprises navigating the AI landscape.
No insights match this filter.
About Nyedis
Born from the Empire State
Two of the IAM industry's most experienced implementation pioneers created the model for enterprise identity strategies—and now bring that same rigor to the AI frontier.
"Two of the IAM industry's most experienced implementation pioneers have teamed up to bring Identity Services cutting-edge technologies—taking the enterprise security ecosystem to new heights never seen in this space."
Our Foundation
"Nyedis has devoted its team to in-depth product research, training, and development of groundbreaking technologies redefining Identity and Access Management v3.0. We provide future solutions for clients stuck with legacy problems."
Our Mission
Leadership
Engineers, advisors, and specialists driving enterprise security forward.
Our Journey
Two industry pioneers created the model for enterprise identity implementation.
Pioneered cloud security architecture as enterprises migrated to AWS and Azure.
Led zero trust transformations for financial services and healthcare sectors.
Started R&D on AI agent security, recognizing agents as a new identity class.
Formalized our AI practice with security-first agent development frameworks.
Leading enterprises into the agentic AI era with battle-tested governance.
Every AI solution carries 20 years of security lessons. We don't bolt on security—we build it in from day one.
We're practitioners, not just advisors. Our team has built and deployed AI systems at enterprise scale.
We don't cut corners on governance, compliance, or best practices. Enterprise AI demands enterprise rigor.
We work alongside your teams, transferring knowledge and building capabilities that outlast our engagement.
Let's discuss how our two decades of security expertise can accelerate your AI initiatives.
CEO / Co-Founder
Ted Balfour leads Nyedis as CEO and Co-Founder, bringing two-plus decades at the intersection of cybersecurity, identity, and technology leadership. As a recognized voice in Identity and Access Management, Ted has shaped how enterprises protect digital assets and govern user access — translating fluently between the technical depth security demands and the business outcomes the C-suite needs. His leadership style fuses architectural rigor with pragmatic execution, which is why he's a trusted advisor to organizations modernizing their identity and AI security posture.
// Direct Contact
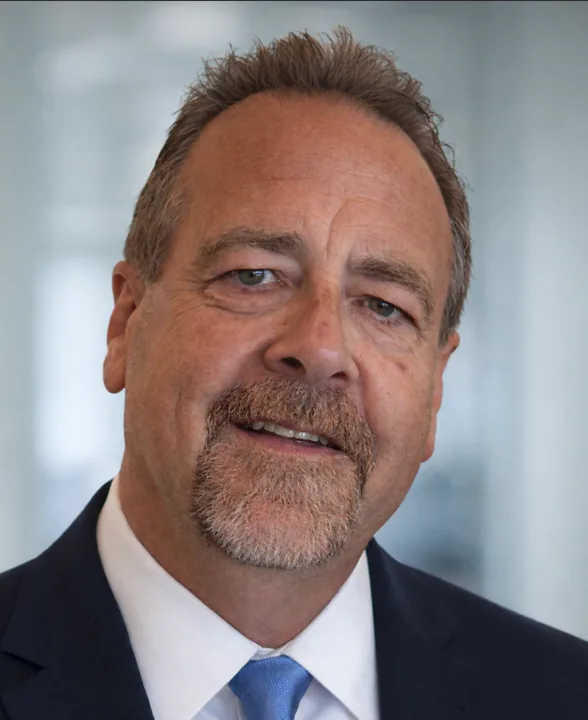
CEO / CO-FOUNDER, NYEDIS
Principal AI & Security Engineer / Architect of Argent Strategic Intelligence
Adam Callen speaks and advises at the intersection of AI and national-scale cybersecurity. He has engineered the identity systems governments depend on — and now builds the control technology that makes autonomous AI safe for serious institutions. Author of The Last Human Job. Member, Forbes Technology Council.
// Direct Contact
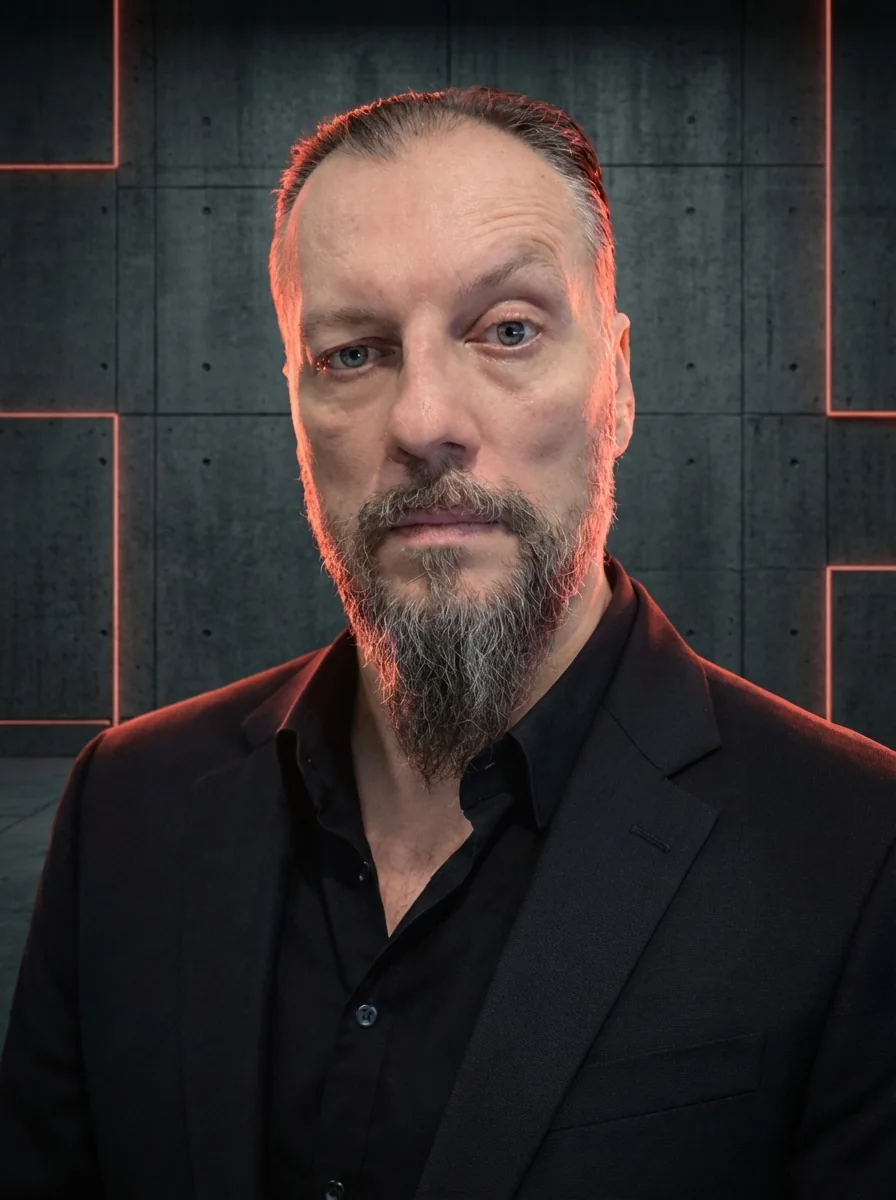
Member, Forbes Technology Council
Speaking & advisory topics
AI agents as a new identity class: authority, evidence, kill-switches.
Governance, risk classification, and operating models leaders can trust.
Lessons from Healthcare.gov, NYC Cyber Command, and 14M-identity environments.
Deepfakes, prompt injection, synthetic fraud, and cognitive defense.
Track record
Identity Management Architect and Operations Lead. Re-architected and stabilized the identity services behind registration and login. Coordinated 80+ engineers, developers and project staff; reported to Todd Park, then Chief Technology Officer of the United States.
Led privileged-access deployment across seven city agencies. Built automation that removed months of engineering effort from deployment.
Identity infrastructure across 22 campuses and more than 250,000 identities.
Managed identity infrastructure serving more than 14 million active users.
Redesigned a production identity environment: monthly operating cost from more than $200,000 to less than $25,000. Also identified more than $75,000 per month in AWS savings.
Reworked the migration of four million users, cutting a process that had taken two weeks to eight hours.
Assessed an identity environment of 100,000+ workforce identities and built a modernization roadmap for a three-to-six-month transformation instead of more than a year.
Reduced projected hardware costs by 66%. At Priority Health, discovery and project analysis cut scope and duration by more than 30%.
Helped build a multimillion-dollar enterprise-services business from the ground up: startup capital, brand, recruiting and training, and winning client engagements.
Architect of Argent Strategic Intelligence: Master Control System. Translated 60 enterprise use cases into repeatable conformance tests and release gates.
Co-founded DeepGreenAI. Its trading systems, built on neural networks, transformer models and generative adversarial networks, moved more than 4% of Coinbase monthly BTC/USD trading volume at their peak.
Developed a token-based authorization system that recorded nearly 18,000 roles and more than 200,000 role interactions in its first three months.
More about Adam
More than 25 years in technology, including over two decades securing enterprise identities and critical infrastructure, together with firsthand experience developing AI systems and turning complex technical capabilities into business solutions.
As CEO, Adam leads company strategy, product direction, enterprise relationships, and the team and operating discipline required to execute. His thesis: AI security cannot be treated solely as a question of what a model says. It must also address who or what is acting, whose authority it is using, which systems it can reach, what information it can access, and whether an organization can intervene before an action becomes a business incident.
Adam is driving the development of Argent as a central control layer for enterprise AI, governing interactions among models, agents, tools, credentials and enterprise data. Under his product direction it covers agent identity and lifecycle management, permission-aware data retrieval, credential brokering, defenses against malicious instructions, data-loss prevention, spending controls, audit evidence, and emergency shutdown.
At Oracle he supported identity infrastructure across federal and Department of Defense environments, including security hardening, vulnerability remediation, and disaster-recovery arrangements involving AWS GovCloud. At Cincinnati Children's Hospital he was responsible for an identity-modernization project and its team from initial delivery planning through final sign-off.
At Johnson & Johnson he delivered AI capability and security seminars and working sessions for technical teams and members of the Worldwide AI Council. For UniFirst he helped establish AI infrastructure and secure development workflows; for Las Vegas Sands he facilitated planning around worst-case AI-enabled cyberattacks. At Discover he led a privileged-access assessment spanning seven vendors, and at JPMorgan Chase he led a team through a cloud API-gateway migration to production.
His AI experience predates his work on enterprise AI governance, and his product work spans cloud-native applications, serverless media-processing systems and digital identity products. More recently he has developed tools for persistent agent sessions, remote approvals, task coordination, human review and validation, plus agent workflows for research, onboarding and business-process automation.
He hosts the Nyedis Anarchy Series, is a member of the Forbes Technology Council, and has joined industry conversations with KuppingerCole on digital identity. Under the IDM Rockstar name he published free identity-management tutorials, and earlier gave lectures on wireless security and hardening for universities and corporations. His roots reach back to early-1990s bulletin-board culture and The Crypt. He holds a Bachelor of Science in Computer Networking and Japanese Linguistics from Eastern Michigan University.
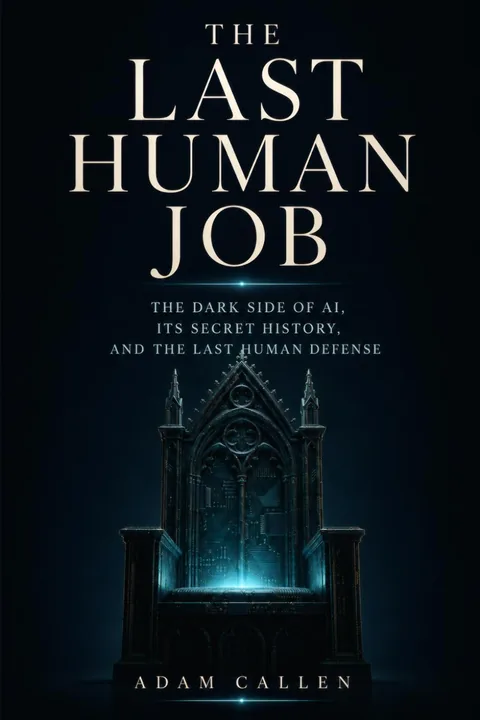
The book
AI's Dark Side, and the Last Human Defense
By Adam Callen
5.0on Amazon5 ratingsThe first continuous history of the AI security war, told one true story at a time, from each breakthrough to the breach that followed it.
The deepfaked video call that walked roughly $25 million out of a global firm while every "executive" on the screen was a forgery. The nation-states already inside the wire. The attack that, by 2027, needs no human hand at all. Every defense you rely on can be handed to a machine. Except one.
Written for the CISO and the CIO, and clear enough for anyone who depends on them.
Selected environments
Principal-level engagements
 U.S. Department of Defense
 Oracle Federal / FedRAMP / DoD
 Healthcare.gov
 NYC Cyber Command
 World Bank
 CUNY
 State of Tennessee
 Maryland Dept. of Education
 PHEAA / Pennsylvania student aid
 JPMorgan Chase
 Bank of America
 HSBC
 UBS
 Wells Fargo
 Capital One
 Banco Itau
 Fannie Mae
 Freddie Mac
 Discover
 Standard & Poor's
 Johnson & Johnson
 Intel
 McAfee
 Allstate
 Becton Dickinson
 Ernst & Young
 Gap
 Creative Artists Agency
 Centene
 Cincinnati Children's
Available for keynotes, executive briefings & advisory engagements
Join Our Team
Join a team of security veterans and AI innovators shaping how enterprises deploy intelligent systems.
Open Positions
Build production AI agent systems for Fortune 500 enterprises.
Design security frameworks for enterprise AI deployments.
Help clients integrate AI solutions with their existing infrastructure.
We're always looking for exceptional talent. Send us your resume and tell us how you'd contribute.
Contact Us
Whether you're exploring AI for the first time or scaling existing deployments, we're here to help. Tell us about your project.
Reach out directly or fill out the form and we'll respond within 24 hours.
Client Success
Real results from organizations that deployed secure, scalable AI solutions with Nyedis.
Financial Services
Needed to deploy AI agents across 50,000+ employees while maintaining regulatory compliance.
85% reduction in manual document processing with zero security incidents.
Healthcare
Required HIPAA-compliant AI integration for patient data analysis.
Deployed AI Sentinel across 12 hospitals with full audit compliance.
Technology
Scaling AI-powered customer support without compromising data privacy.
3x faster resolution times with enterprise-grade security controls.
Let's discuss how Nyedis can help your organization achieve similar results.
Live Workshop // Limited Seats
Stop experimenting. Start deploying Claude Code with enterprise-grade security, governance, and scale. One intensive workshop that transforms how your organization builds with AI.
March 2026 // Virtual Live // Led by Adam Callen, CIO @ Nyedis
claude-code — enterprise-init
$claude --enterprise init
✓MCP server connections established (3/3)
✓Security policy loaded: enterprise-strict
✓Governance hooks configured
✓Audit logging enabled → s3://sentinel-logs
✓Token budget: 500K/session | Cost controls: active
⚡Enterprise Claude Code ready.
█ Type your first prompt...
Who Is This For
This workshop delivers immediate, actionable value for leaders who need to move fast—without moving recklessly.
Align AI deployment with business strategy. Understand total cost of ownership, security posture, and governance frameworks before scaling.
Go beyond toy demos. Learn production patterns for MCP servers, custom tool chains, and enterprise-grade agent architectures that your teams can maintain.
Deploy AI without compromising your security posture. Master audit logging, policy enforcement, and compliance-ready configurations from day one.
Curriculum
Configure Claude Code with least-privilege access, audit trails, and policy enforcement that satisfies your security team.
Build custom Model Context Protocol servers that connect Claude to your internal APIs, databases, and tools—securely.
Implement token budgets, cost controls, and approval workflows that give leadership visibility without slowing teams down.
Move from prototype to production with patterns for CI/CD integration, monitoring, error handling, and team onboarding.
Enterprise security model, MCP architecture overview, and environment setup with your own Claude Code instance.
Hands-on: create a production MCP server, configure governance hooks, and connect to simulated enterprise systems.
CI/CD pipeline setup, monitoring dashboards, cost controls, and audit logging configuration.
Team rollout playbook, change management strategy, and ongoing governance framework for autonomous AI operations.
Outcomes You Can Expect
Leave with a production-ready Claude Code configuration tailored to your enterprise's security requirements.
A proven rollout playbook for onboarding engineering teams without creating shadow AI or compliance gaps.
Governance frameworks that protect the organization while keeping developers productive and autonomous.
Cost tracking, usage analytics, and outcome measurement frameworks to prove value to leadership.
What's Included
4-hour intensive session with hands-on exercises, live Q&A, and real-time troubleshooting.
Pre-built security policies, governance hooks, and MCP server templates ready for your environment.
Full access to all workshop code, examples, and reference architectures on GitHub.
Bring your core team. One registration covers up to 5 participants from the same organization.
Step-by-step enterprise security checklist covering audit, compliance, and incident response.
Direct Slack access to the instructor for implementation questions after the workshop.
March 2026 // 10AM–2PM ET // Virtual Live
$2,497per team
Up to 5 seats per registration
Reserve Your Team's SeatsLimited to 25 seats for hands-on engagement
Adam Callen
CIO @ Nyedis
"I've spent 20 years deploying enterprise technology—from IAM platforms to cloud migrations. Claude Code is the most transformative tool I've seen since Kubernetes, but only if you deploy it right. Most teams are using it like a fancy autocomplete. This workshop shows you how to turn it into an enterprise-grade development platform with the security, governance, and scale your organization demands."
20+ years enterprise IT • Former CTO • AI security specialist
FAQ
Register Now
Limited to 25 participants. Register now to guarantee your team's spot.
Questions? Email ai@nyedis.com
Legal
Last updated: February 1, 2026
We collect information you provide directly, such as your name, email address, and company information when you sign up for our services, request a demo, or contact us. We also collect usage data and analytics to improve our services.
We use collected information to provide and improve our services, communicate with you about your account and our offerings, and ensure the security of our platform. We never sell your personal information to third parties.
As an enterprise security company, we implement industry-leading security measures to protect your data. This includes encryption at rest and in transit, regular security audits, and compliance with SOC 2 Type II standards.
You have the right to access, correct, or delete your personal information. You may also opt out of marketing communications at any time. Contact us at privacy@nyedis.com for any privacy-related requests.
If you have questions about this Privacy Policy, please contact us at privacy@nyedis.com or through our contact page.
Legal
Last updated: February 1, 2026
By accessing or using Nyedis services, you agree to be bound by these Terms of Service. If you do not agree to these terms, you may not use our services.
Our services are provided for lawful business purposes only. You agree not to use our services for any illegal or unauthorized purpose, or in any way that could damage, disable, or impair our systems.
All content, features, and functionality of our services are owned by Nyedis and are protected by international copyright, trademark, and other intellectual property laws.
Nyedis shall not be liable for any indirect, incidental, special, consequential, or punitive damages resulting from your use of or inability to use our services.
We reserve the right to modify these terms at any time. We will notify you of any changes by posting the new Terms of Service on this page.
For questions about these Terms of Service, please contact us at legal@nyedis.com.